Checklist for NetScaler (Citrix ADC) CVE-2025-5777 & CVE-2025-6543

On June 17, 2025, Citrix published a security advisory for CVE-2025-5777, followed by CVE-2025-6543 on June 25, 2025. Both are classified as critical and are actively being exploited in the wild.

Current notice: This article covers a specific older NetScaler vulnerability. For a vendor-independent process covering current CVEs, firmware updates and checks for possible compromise, refer to our NetScaler CVE Checklist.

Threat Overview

  • CVE-2025-5777: Critical vulnerability due to improper input validation → leads to memory overread
  • CVE-2025-6543: Enables memory overflow, potentially resulting in DoS or arbitrary code execution → Exploits available !

⚠️ Important: Simply applying the firmware update is not enough. You must manually terminate all active ICA and PCoIP sessions after patching to ensure the vulnerability is fully mitigated.

Continue reading “Checklist for NetScaler (Citrix ADC) CVE-2025-5777 & CVE-2025-6543”

Checklist for NetScaler (Citrix ADC) CVE-2023-4966

Citrix issued an alert (10/10/2023) about a critical vulnerability (CVE-2023-4966) in all NetScaler (Citrix ADC) & Gateway systems. Several working exploits have been published.

Current notice: This article covers a specific older NetScaler vulnerability. For a vendor-independent process covering current CVEs, firmware updates and checks for possible compromise, refer to our NetScaler CVE Checklist.

Please note that simply updating the systems is not enough. The connection tokens must also be reset.

Important ! There are no patches for NetScaler (Citrix ADC) version 12.1 or older. These systems have reached their EOL and will therefore no longer be equipped with the necessary fix. In this case please update to the latest 13.0, 13.1 or 14.1 version.

The vulnerability allows anonymous remote code execution and thus unauthenticated attackers to take over various machines with root privileges.

Continue reading “Checklist for NetScaler (Citrix ADC) CVE-2023-4966”

Checklist for NetScaler (Citrix ADC) CVE-2023-3519

Citrix issued an alert yesterday (07/18/2023) about a critical vulnerability (CVE-2023-3519) in all NetScaler (Citrix ADC) & Gateway systems. To date, no working exploits have been published.

Current notice: This article covers a specific older NetScaler vulnerability. For a vendor-independent process covering current CVEs, firmware updates and checks for possible compromise, refer to our NetScaler CVE Checklist.

Important ! There are no patches for NetScaler (Citrix ADC) version 12.1 or older. These systems have reached their EOL and will therefore no longer be equipped with the necessary fix. In this case please update to the latest 13.0 or 13.1 version.

The vulnerability allows anonymous remote code execution and thus unauthenticated attackers to take over various machines with root privileges.

As we hear from the Citrix community, more and more attacked systems are being found. The first exploits have also been available for purchase on the dark web for some time.

Continue reading “Checklist for NetScaler (Citrix ADC) CVE-2023-3519”

Web Authentication Action in NetScaler

On one of my recent deployments, I needed to set up external access using NetScaler to an internally hosted web application (Grafana).

Grafana is a cross-platform open source application for graphical representation of data from various data sources such as InfluxDB, MySQL, PostgreeSQL, Prometheus and Graphite.

The challenge here was that the customer wanted to pre-install authentication on the NetScaler, but the users were only known to the web application itself.

The question that therefore came to me was:
How can I check the user of the web application if only the web application itself has access to the user data?

I had only used standards like LDAP, RADIUS, CERT, SAML etc. for user authentication on NetScaler, but these were not useful here because the target system should not be changed.

Continue reading “Web Authentication Action in NetScaler”

Citrix ADC 101 – Fundamentals

The following is a collection of basic information about Citrix ADC. From licensing, to the most important commands, to the update procedures that can be performed.

General Information

Here is some basic information about Citrix ADC.

Operating System and Architecture

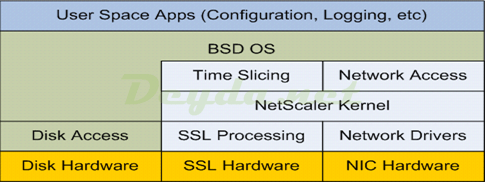
Citrix ADC is based on the open source operating system FreeBSD. Unlike the very similar Linux, FreeBSD has a modular kernel and Citrix has taken advantage of this to modify FreeBSD’s Bash shell by removing the networking subsystem and replacing it with its own. The modifications were placed in a custom kernel module called NetScaler Core Packet Processing Engine (PPE).

Citrix ADC FreeBSD
Continue reading “Citrix ADC 101 – Fundamentals”