Workaround after Remote Assistance Error

After installing the January 2026 Microsoft security updates, Remote Assistance (msra.exe) no longer works on multiple Windows versions. This directly affects Citrix Director Shadowing, as the generated invite files can no longer be opened on patched systems.

The issue is caused by a security hardening related to CVE-2026-20824 – Windows Remote Assistance Security Feature Bypass Vulnerability. While the fix is technically correct from a security perspective, it currently breaks legitimate Remote Assistance workflows in enterprise environments.

Continue reading “Workaround after Remote Assistance Error”

Web Authentication Action in NetScaler

On one of my recent deployments, I needed to set up external access using NetScaler to an internally hosted web application (Grafana).

Grafana is a cross-platform open source application for graphical representation of data from various data sources such as InfluxDB, MySQL, PostgreeSQL, Prometheus and Graphite.

The challenge here was that the customer wanted to pre-install authentication on the NetScaler, but the users were only known to the web application itself.

The question that therefore came to me was:
How can I check the user of the web application if only the web application itself has access to the user data?

I had only used standards like LDAP, RADIUS, CERT, SAML etc. for user authentication on NetScaler, but these were not useful here because the target system should not be changed.

Continue reading “Web Authentication Action in NetScaler”

SAML Authentication between Citrix & Microsoft with Azure MFA

Update to the latest cloud navigation.

As a result of increasing projects, here is a little how-to with the summary of my previous articles. The main points are:

  • Azure AD Seamless Single Sign-On (PTA / PHS)
  • SAML Authentication (Azure AD as IdP & Citrix Gateway as SP)
  • Citrix Federated Authentication Service (FAS)
  • Microsoft Azure Multi-Factor-Authentication with Conditional Access

Requirements

  • Fully working Citrix Virtual Apps and Desktop Environment (StoreFront & DDC Minimum Version 7.9)
  • NetScaler with successful base configuration & activated Enterprise or Platinum license (Minimum Version 12.1 Build 50+ for native workspace app, for browser Minimum Version 11.1)
  • Configured Unified Gateway vServer
  • Internal and external DNS entries for Unified Gateway vServer (e.g. citrix.deyda.net)
  • Certificates for DNS entries (wildcard certificates are the easiest)
  • Existing Azure Tenant with Azure-AD base configuration (Domain, AAD Sync) & activated Azure AD Premium license
  • AD Connect version installed and configured (Minimum Version 1.1.644.0)
  • Firewall release for *.msappproxy.net on port 443
  • Domain administrator credentials for the domains that connected to Azure AD via AD Connect
  • Installed Authenticator App on Test User Mobile Phone
Continue reading “SAML Authentication between Citrix & Microsoft with Azure MFA”

Citrix ADC 101 – Fundamentals

The following is a collection of basic information about Citrix ADC. From licensing, to the most important commands, to the update procedures that can be performed.

General Information

Here is some basic information about Citrix ADC.

Operating System and Architecture

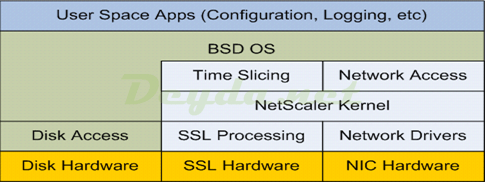
Citrix ADC is based on the open source operating system FreeBSD. Unlike the very similar Linux, FreeBSD has a modular kernel and Citrix has taken advantage of this to modify FreeBSD’s Bash shell by removing the networking subsystem and replacing it with its own. The modifications were placed in a custom kernel module called NetScaler Core Packet Processing Engine (PPE).

Citrix ADC FreeBSD
Continue reading “Citrix ADC 101 – Fundamentals”

Why a Windows Server 2019 VDI should be Hybrid Azure AD joined

What is Hybrid Azure AD Join ?

Let’s just start with the official definition from the Microsoft documentation:

Hybrid Azure AD Join: Joined to on-premises AD and Azure AD requiring organizational account to sign in to the device.

This means that after the device is Hybrid Azure AD joined, it behaves the same as any other computer connected to Active Directory.

Sign in with an Active Directory account is required.
User credentials are verified against an Active Directory domain controller.
Group Policy objects for users & computers read from the domain controller are applied automatically.

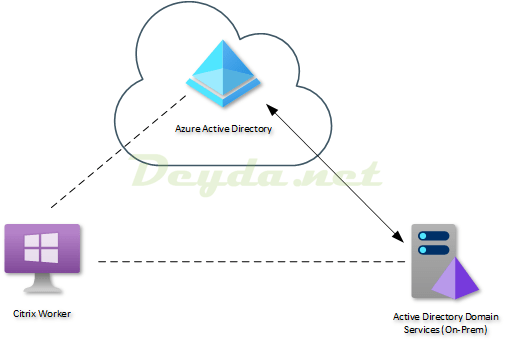
Hybrid Azure AD Join

After the Active Directory connection process is complete, additional steps are performed asynchronously in the background to register the device in Azure AD as well.

Continue reading “Why a Windows Server 2019 VDI should be Hybrid Azure AD joined”